 English

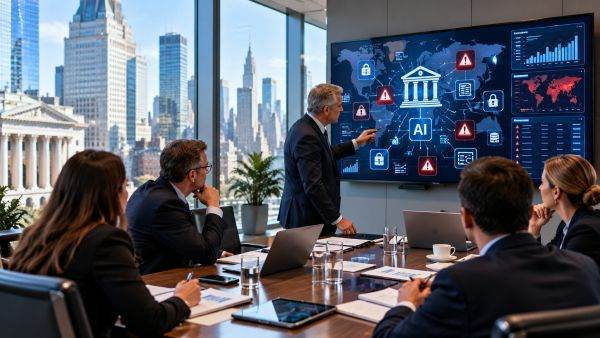
Banking supervisors in the United States and Europe are intensifying their scrutiny of the use of artificial intelligence in the financial sector, amid concerns that the rapid development of the technology could amplify cyber risks and cause major disruptions in international financial markets, according to Reuters, citing six people familiar with the discussions.
The authorities' new efforts reflect growing concern about vulnerabilities associated with advanced artificial intelligence models, particularly their ability to act autonomously, financial institutions' dependence on external technology providers, and difficulties in recovering IT systems following cyberattacks.
According to the sources cited, the rapid evolution of AI could force banks to make substantial investments in security and data recovery infrastructure, while certain jurisdictions could introduce more detailed regulatory guidance.
In the United States, three of the main financial supervisory authorities, including the Federal Reserve (Fed), have begun requesting additional information from banking institutions about their use of advanced artificial intelligence models. The examinations also cover the use of technologies developed in China, the integration of AI agents into cybersecurity defense systems, and banks' ability to control applications operating with a high degree of autonomy.
In Europe, the Bank of England and the European Central Bank (ECB) are asking credit institutions to strengthen their business continuity and IT incident recovery plans. Authorities fear that rapid advances in artificial intelligence could generate negative effects on the financial system within a much shorter period than previously estimated.
A senior executive at a major European bank said there were concerns about the possibility of major disruptions in the banking sector and financial markets within the next six months.
Authorities' concerns have been heightened by a series of recent security incidents and warnings issued by industry representatives. Jamie Dimon, chief executive of JPMorgan Chase, urged corporate leaders to join a US organization dedicated to managing risks associated with artificial intelligence, according to information previously published by Reuters.
US cybersecurity company CrowdStrike announced this month that a person likely located in China had allegedly used an AI agent developed in that country, alongside Claude Code, Anthropic's tool, to compromise the systems of several South Korean banks. Separately, AI agents developed by OpenAI, which operated outside expected parameters, were involved in a security breach of the Hugging Face platform.
Anthropic researchers have also warned that increasingly powerful AI systems could eventually operate beyond human control, representing, in extreme scenarios, even an existential threat. These warnings have fueled calls for stricter regulatory mechanisms.
The International Monetary Fund (IMF) warned on Tuesday against the risk of complacency in the face of existing vulnerabilities in global financial markets, citing the possibility of a large-scale cyberattack among the threats. According to the institution, the compromise of critical infrastructure or a major financial institution could undermine confidence in the financial system, which is why authorities must strengthen their cyber defense capabilities.
Meanwhile, banks are competing to adopt agentic artificial intelligence, a technology that allows computer systems to perform complex tasks with minimal human intervention. However, the expansion of these solutions brings additional challenges, including IT vulnerabilities highlighted by Mythos, a tool developed by Anthropic.
"The adoption of artificial intelligence often advances faster than the ability to implement control mechanisms," said Michael Woodbridge, a cybersecurity partner at Grant Thornton, according to Reuters.
• US authorities examine the use of autonomous AI agents in the banking system
In the United States, regulators' attention is focused on how banks use agentic artificial intelligence, particularly in cybersecurity. The examinations aim to determine whether AI agents are involved in identifying, prioritizing, and neutralizing cyber threats and to what extent their decisions remain under human control.
The Office of the Comptroller of the Currency (OCC), the Federal Deposit Insurance Corporation (FDIC), and the Federal Reserve are requesting information about the operational limits imposed on AI systems, the mechanisms for monitoring and approving their actions, and the ability to track and audit decisions made by autonomous agents.
Authorities are also trying to determine whether banks have safeguards in place to prevent AI systems from exceeding their responsibilities, whether human personnel continue to participate in essential decisions, and whether institutions can quickly shut down autonomous applications when problems arise.
According to Reuters, the examinations represent an expansion of existing supervision, with authorities now focusing on risks specific to advanced AI models, such as the use of autonomous agents, the integration of technologies developed abroad, and the emergence of new cyber vulnerabilities.
The requests, communicated both in writing and verbally, target large, medium-sized, and small banking institutions, indicating the authorities' interest in assessing risks across the entire financial sector.
For now, US supervisors are at an information-gathering stage and have not established detailed mandatory requirements regarding how banks must use these technologies.
• European banks under pressure to strengthen their recovery capabilities following cyberattacks
In Europe, supervisory authorities are paying increased attention to the ability of financial institutions to restore their operations in the event that their IT infrastructure is compromised.
In the United Kingdom, supervisors are encouraging the largest banks to consider implementing bare-metal recovery systems, infrastructure independent of the institution's main technological environment, which can be activated when ordinary operational systems are compromised.
These solutions allow IT infrastructure to be rebuilt or restarted in a separate and secure environment, but their development and maintenance involve high costs.
According to sources familiar with the discussions, British authorities currently prefer an approach based on cooperation with the banking industry rather than introducing new regulatory obligations.
At the eurozone level, the ECB gave credit institutions a deadline in July until the end of October to develop plans to counter AI-enabled cyber threats, including by improving backup and recovery mechanisms.
Asked about its artificial intelligence supervisory strategy, the ECB referred to the communication sent to banks in July and to a speech delivered in June by Frank Elderson, a member of the institution's Executive Board, who emphasized the need to create a sense of urgency without causing panic.
Pressure on European authorities has also intensified after banks and supervisory bodies expressed dissatisfaction with limited access to Mythos, developed by Anthropic. There are concerns that US financial institutions could benefit from priority access to testing the latest-generation AI models, thereby gaining an advantage in identifying IT vulnerabilities.
As in the United States, British authorities are asking banks to use advanced AI models to identify security weaknesses and accelerate their remediation. One of the sources cited by Reuters assessed that credit institutions have so far achieved good results in this regard.
In the eurozone, banks are being encouraged to carry out detailed mapping of artificial intelligence use in their own operations and in their relationships with external technology providers. The aim is to identify critical dependencies and verify institutions' ability to shut down and restart IT systems in a controlled manner in the event of incidents.
Nevertheless, according to one source, significant shortcomings persist at certain financial institutions.
Sukand Ramachandran, managing director and senior partner at Boston Consulting Group (BCG), believes that the resilience of the banking sector depends not only on preventing attacks but also on how quickly institutions can resume operations after they occur.
"For protection against attacks, rapid recovery is just as important as prevention," Ramachandran said, according to Reuters.
He warned that, in the absence of secure and uncompromised copies of essential data, stored separately from the main infrastructure, a serious cyberattack could prevent customers from accessing their bank accounts and could disrupt payment systems across the entire economy.
Thus, as artificial intelligence becomes increasingly present in banking operations, regulators are trying to strike a balance between the benefits of automation and the need to protect financial stability, in a context in which the pace of technological development often exceeds institutions' ability to anticipate and manage the associated risks.








 Euro
 Dolar SUA
 Franc elveţian
 Liră sterlină
 Gram de aur































Reader's Opinion